
This is my write-up on THM’s Windows Event Logs Room.
Answer the questions below
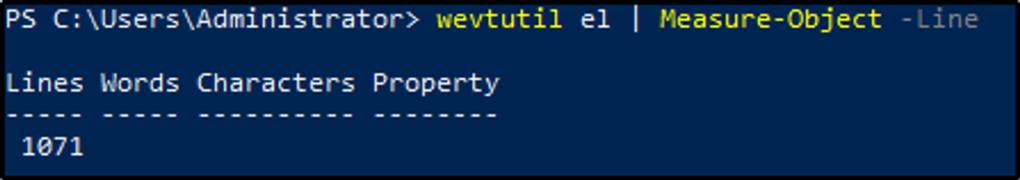
How many log names are in the machine?
The command el would list the log names and the results would then be piped to the next command to count the list of log names by line.
wevtutil el | Measure-Object -Line
What event files would be read when using the query-events command?
Answer: event log, log file, structured query

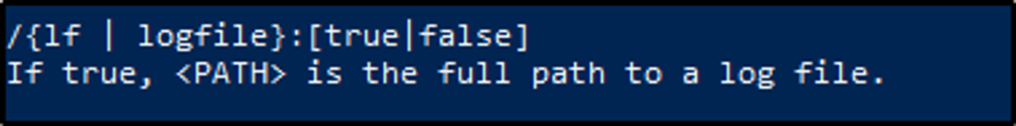
What option would you use to provide a path to a log file?
After running the command, we see the options we can use with qe. The option we would use to include a log file path is /lf:true.
What is the VALUE for /q?
Answer: query XPATH
Scrolling through the options, we can see the value for /q? is XPATH query.

The questions below are based on this command: wevtutil qe Application /c:3 /rd:true /f:text
What is the log name?
From the command given to us, wevtutil is querying events from Application logs.
What is the /rd option for?
Answer: event read redirection
When we run wevtutil qe /?, we would see the options for this command. /rd would refer to event read redirection.

What is the /c option for?
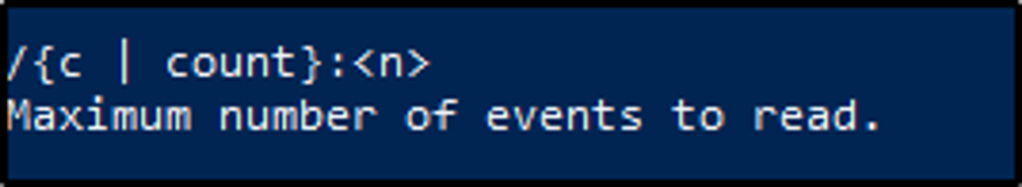
Answer: Maximum number of events to read
/c option refers to the number of events that we wold want to query from the logs.
What are event logs?
But for blue teams, windows event logs serve a different purpose. These logs are analyzed for malicious activities or indicators of compromise. Windows Event Logs can also be forwarded to SIEMs where analyst can aggregate, analyze, and correlate log data from various sources to provide security insights of a network.
For a Linux system, the logging system is knows as Syslog.
Event IDs
With the large number of Event IDs in use, we will definitely need resources to help us monitor and hunt events. This section will be covering us in that aspect.
First on the list is The Windows Logging Cheat Sheet (Windows 7 – Windows 2012). The last version update is October 2016, but it’s still a good resource. The document covers a few things that need to be enabled and configured and what event IDs to look for based on different categories, such as Accounts, Processes, Log Clear, etc.
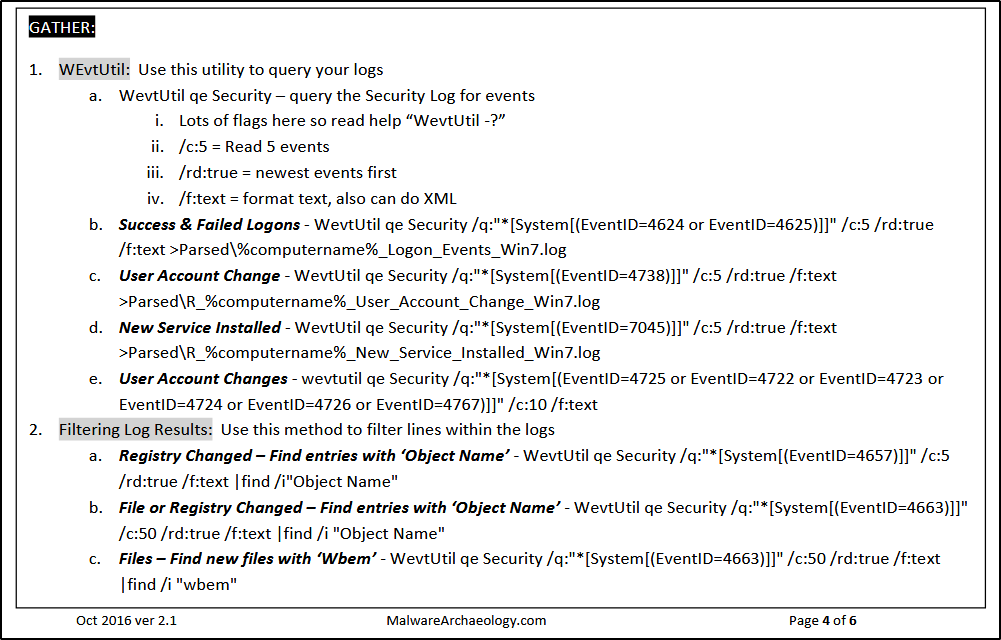
wevtutil qe System /q:"*/System[EventID=7045]" /c:5 /rd:true /f:text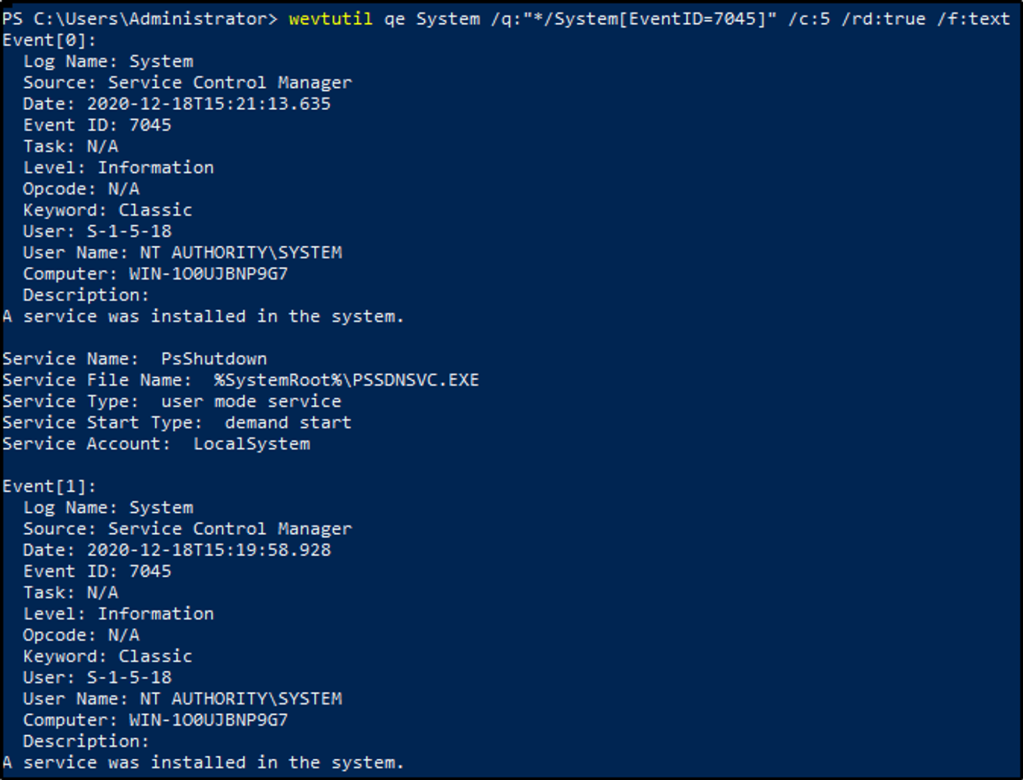
Spotting the Adversary with Windows Event Log Monitoring is another resource.
I was unable though to connect and download the resource.
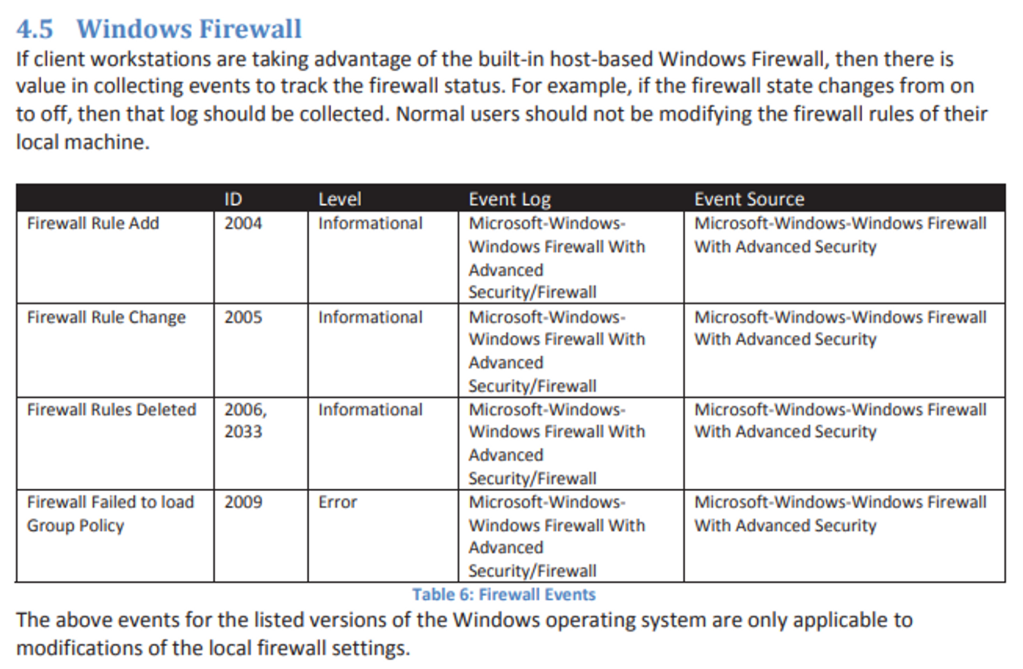
But from the room, a snippet is provided from the document where we see Event IDs related to Firewall Rules.
MITRE ATT&CK is also on the list for monitoring or hunting Event IDs.
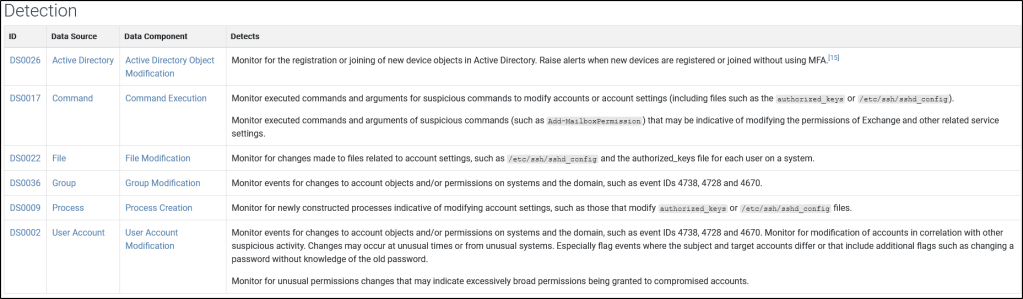
We can look at a Technique and identify the related Event IDs that we should monitor and hunt. For example, if we look at ATT&CK ID T1098 (Account Manipulation), the “Detection” section contains the Event IDs that are triggered.
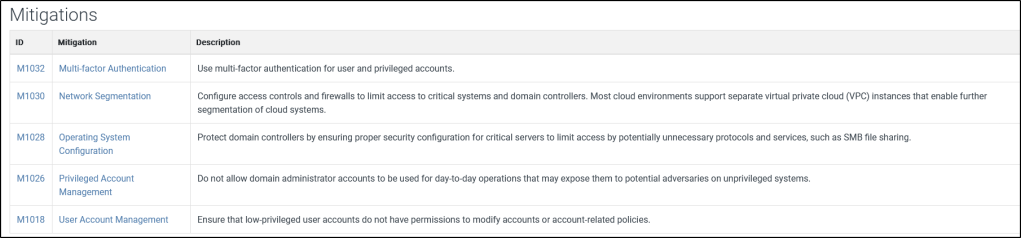
The MITRE ATT&CK framework also contains information on how to mitigate each techniques.
The last two resources are from Microsoft:
- Events to Monitor (Best Practices for Securing Active Directory)
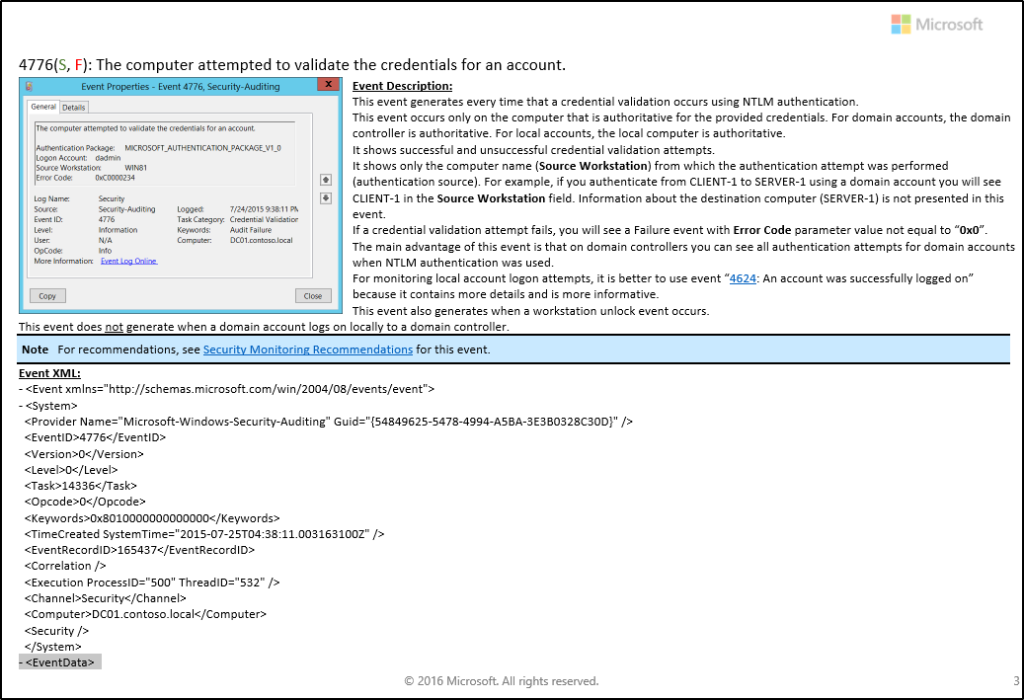
- The Windows 10 and Windows Server 2016 Security Auditing and Monitoring Reference (a comprehensive list [over 700 pages])
- Here is a snippet of the 700-page Windows 10 and Windows Server 2016 Security Auditing and Monitoring Reference
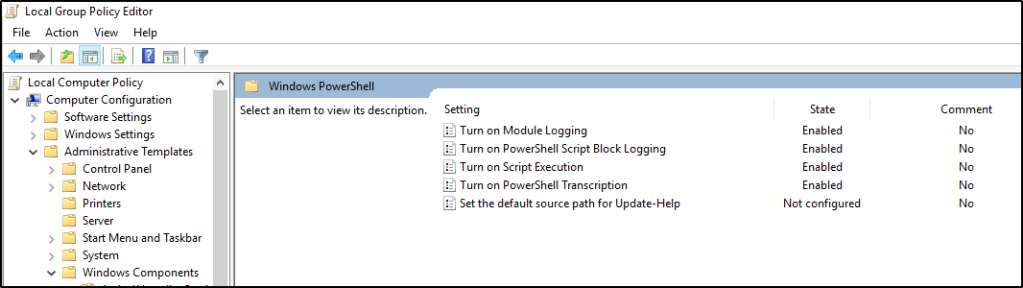
Note: There are certain events that are not generated by default, one of them is PowerShell logging. This feature can be enabled via Group Policy or the Registry.
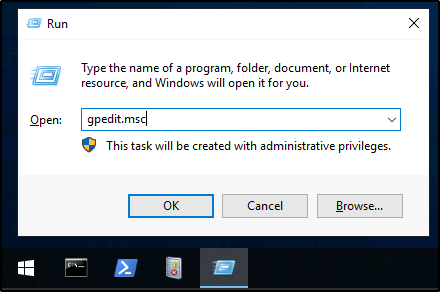
Press the Windows icon on the keyboard + R to open the Run dialog and type gedit.msc to open the Group Policy Management Console.
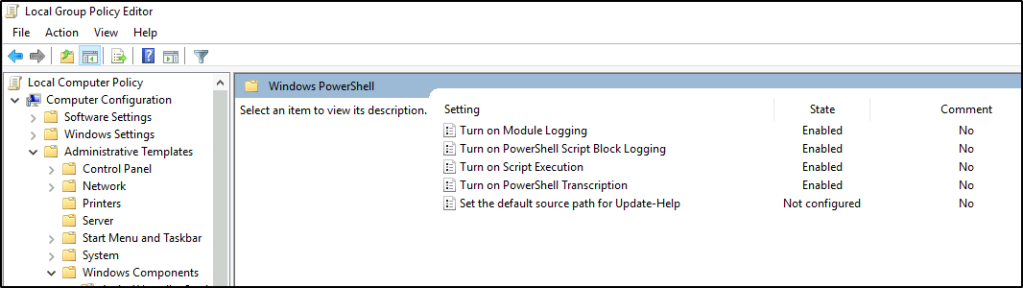
Some resources to provide more information about enabling this feature, along with its associated event IDs:
Another feature to enable/configure is Audit Process Creation, which will generate event ID 4688 and will allow command-line process auditing.
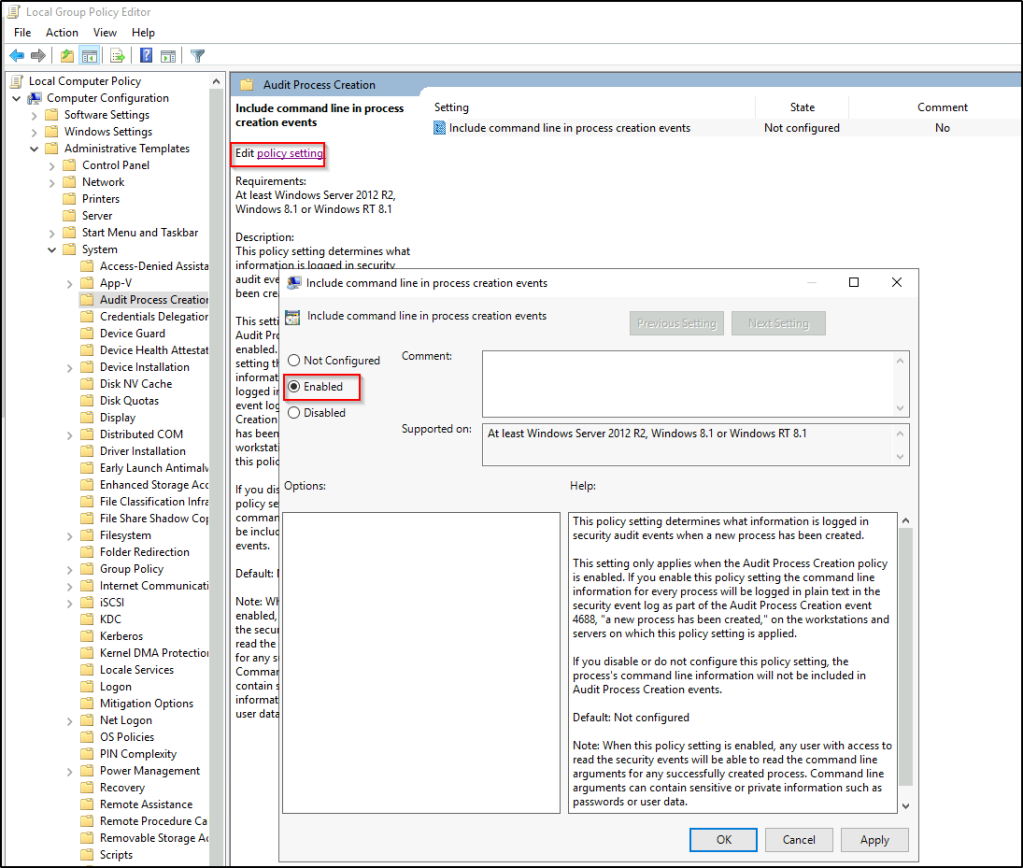
We have already enabled Audit Process Creation
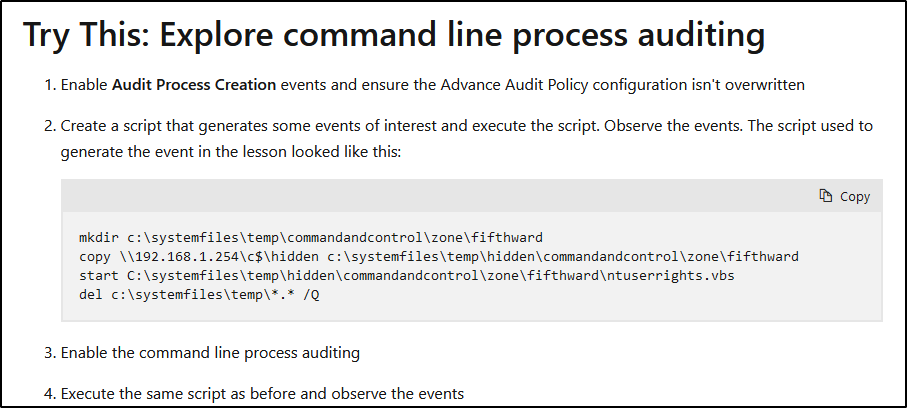
We will now perform step 2.
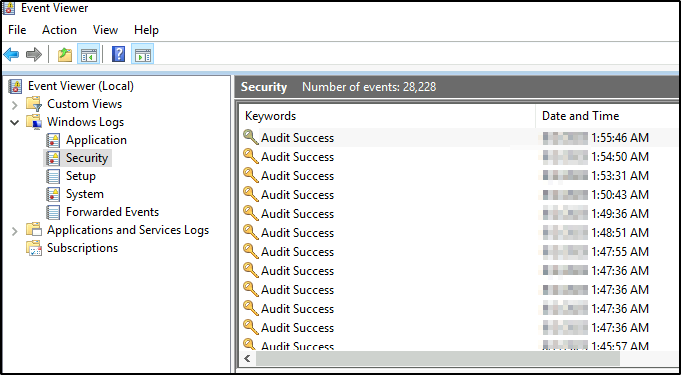
I run a simple command of whoami

Go to Event Viewer to see if the command was logged. We should look under Windows Logs > Security. It can be observed that it was not logged at all.
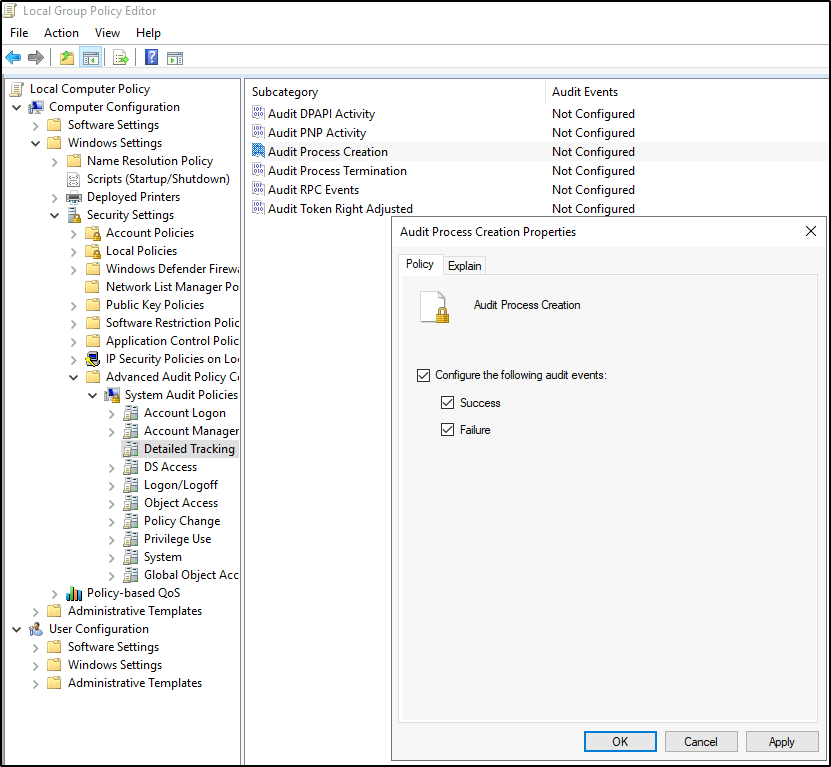
Now for step 3, Enable the command line process auditing.
- In the Group Policy Editor, go to “Computer Configuration” > “Windows Settings” > “Security Settings” > “Advanced Audit Policy Configuration” > “Audit Policies” > “Detailed Tracking.”
- In the right pane, locate the “Audit Process Creation” policy, and double-click on it to open the properties.
- In the properties window, select the “Define these policy settings” option.
- Check the “Success” and “Failure” boxes to enable auditing for successful and failed process creations. Click Apply and Ok.
We’ll run the same command and notice if there’s a difference.
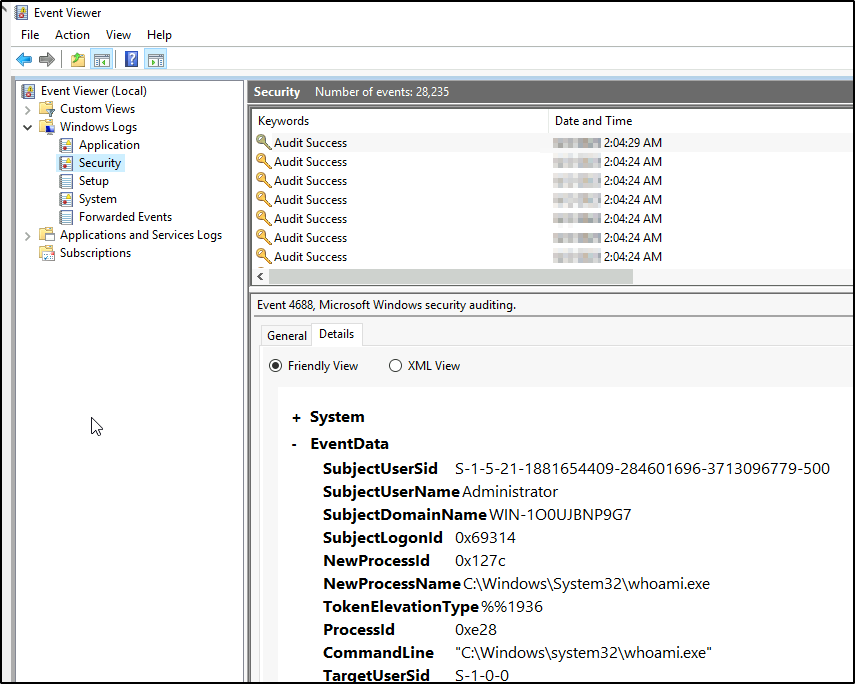
The command was logged this time.
The steps to test the configuration are at the bottom of the document.
To effectively monitor and hunt, we need to know what to look for.
Answer the questions below
Open the merged.evtx file with event viewer
What event ID is to detect a PowerShell downgrade attack?
A search on google would yield us about detecting PowerShell downgrade attacks. Here is an interesting article why attackers would downgrade to older versions of PowerShell.

Answer: 12/18/2020 7:50:33 AM
I used PowerShell for this task, added –Path parameter to indicate the source of the log file.
Get-WinEvent -Path .\\Desktop\\merged.evtx -FilterXPath '*/System/EventID=400' -MaxEvents 10
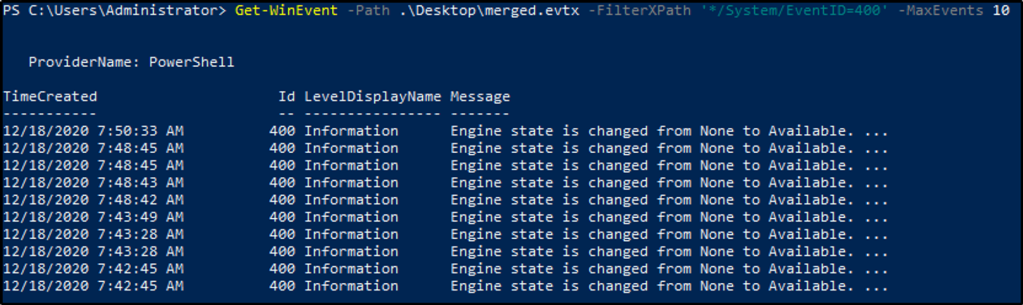
Sort-Object -Property TimeCreated -Descending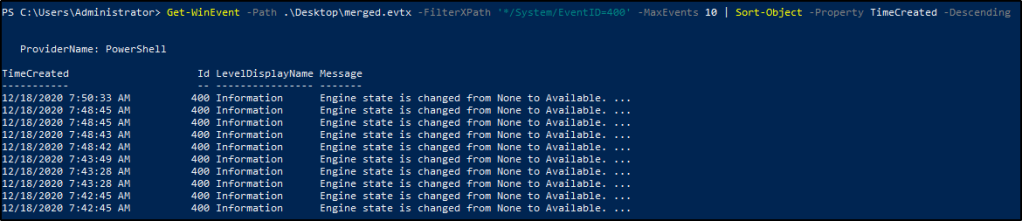
A Log clear event was recorded. What is the ‘Event Record ID’?
In one of the resources provided, an EventID of 104 is generated when the Application or System log were cleared.
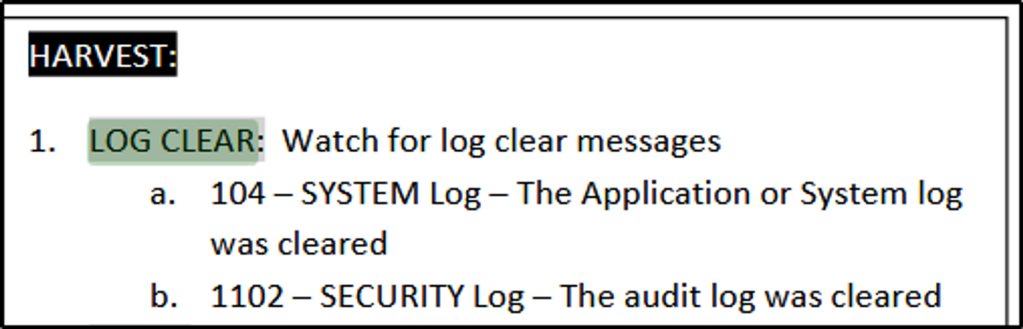
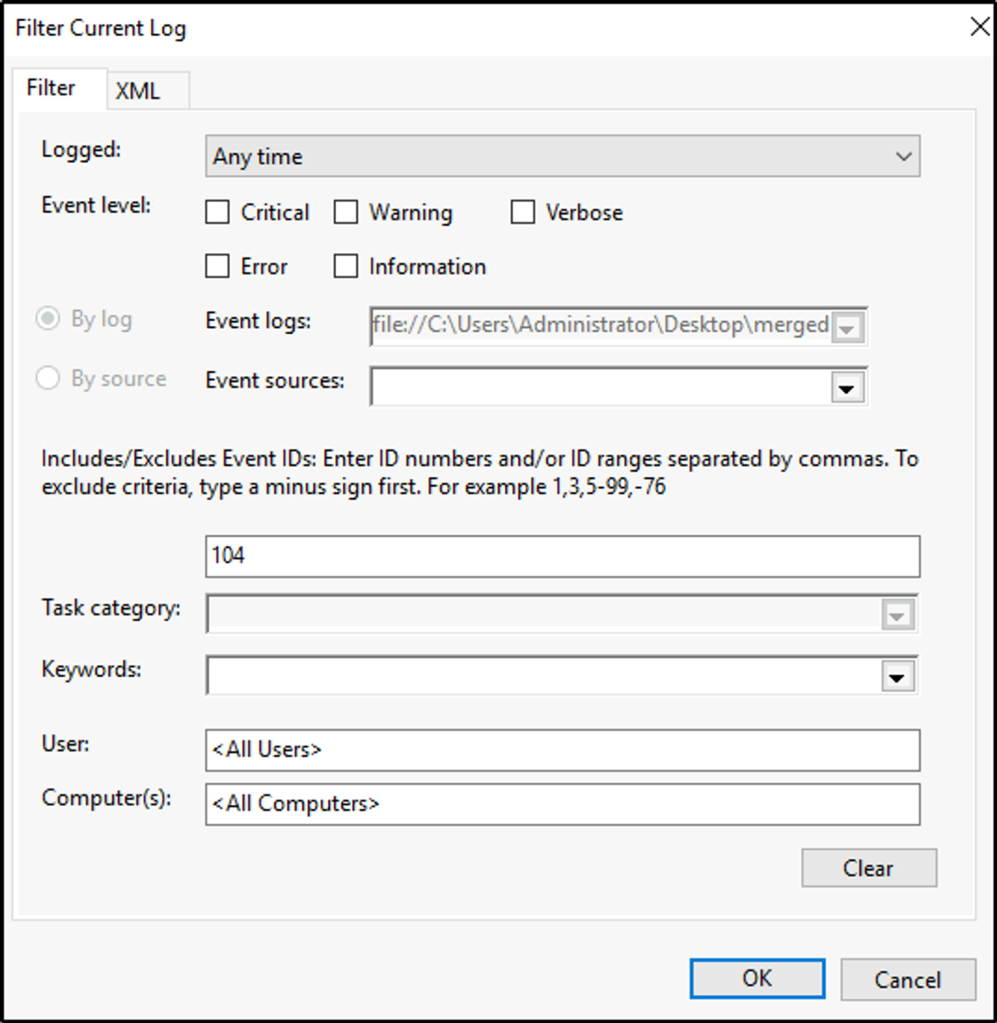
Now that we know the Event ID, let’s filter the logs with eEentID 104.
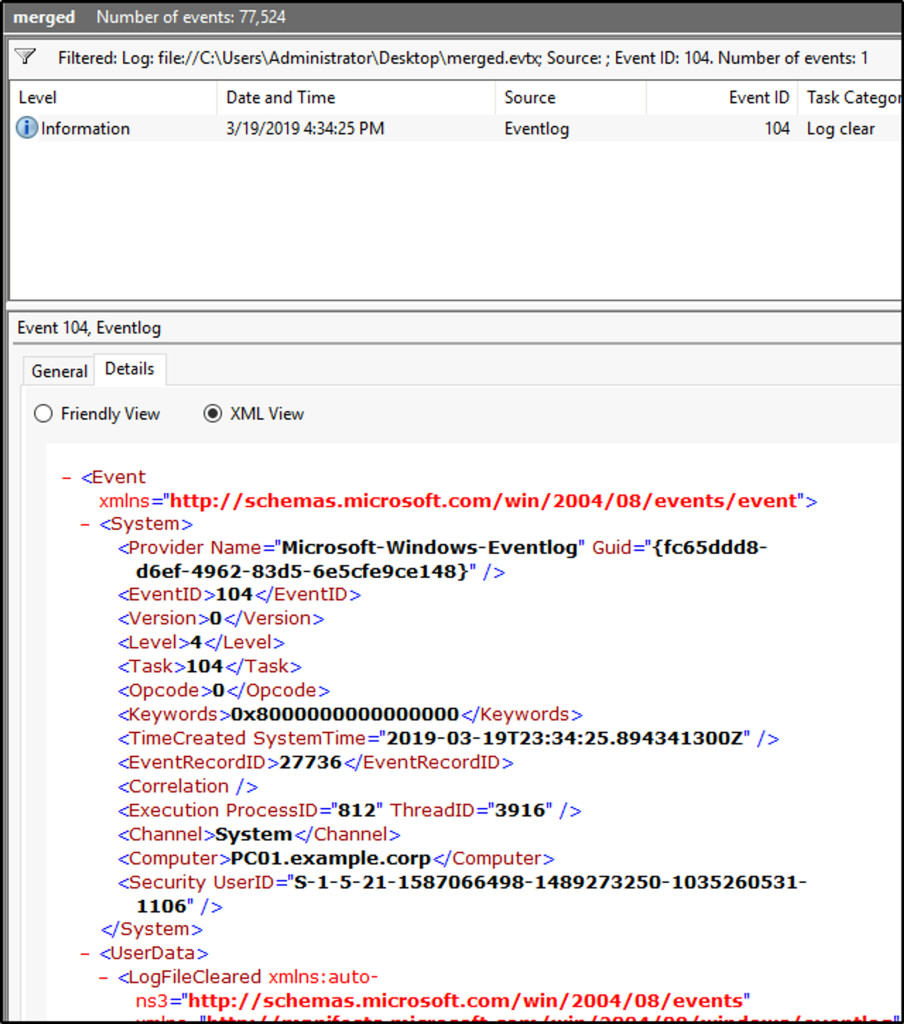
Select the windows event. In the lower pane, click on the “Details” tab and select “XML View”. We now see the ID for the recorded event.
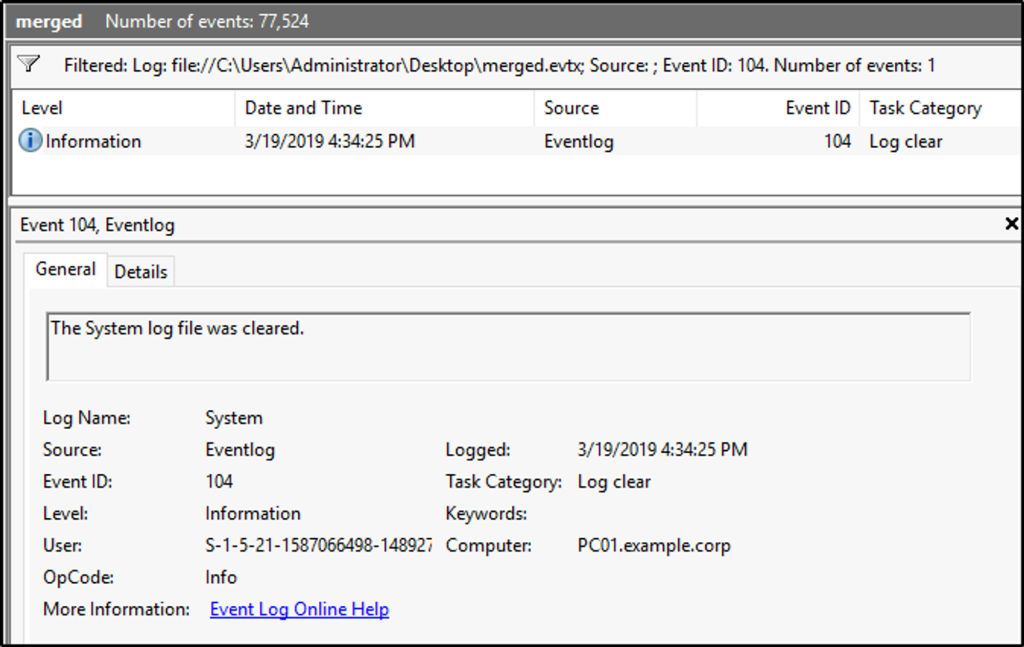
What is the name of the computer?
The computer name is seen in the tag “Computer” or in the “General” tab.
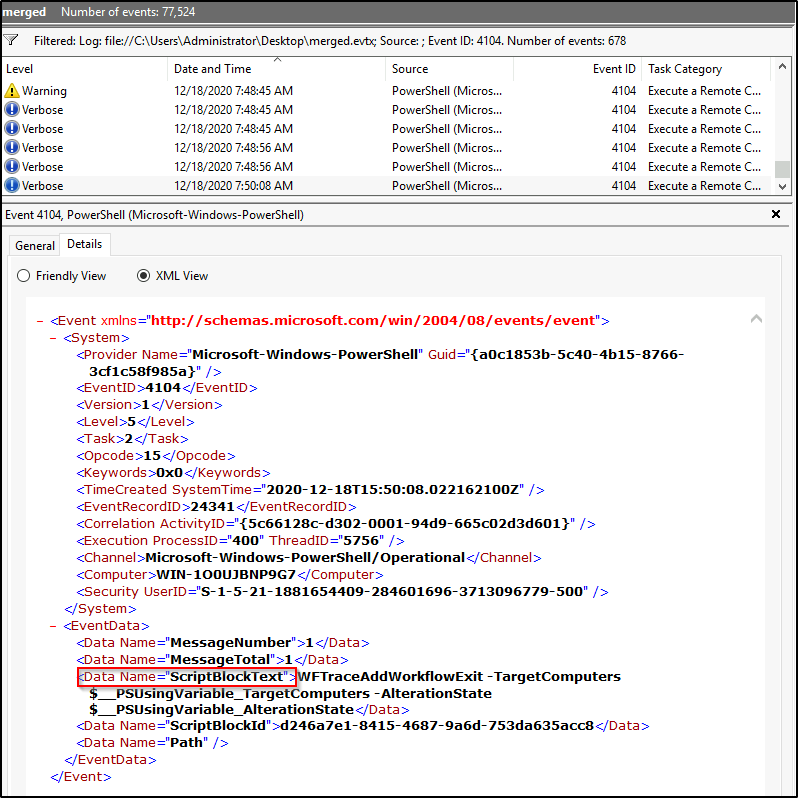
What is the name of the first variable within the PowerShell command?
Get-WinEvent -Path .\\Desktop\\merged.evtx -FilterXPath '*/System/EventID=4104 and */EventData/Data[@Name="ScriptBlockText"]' -Oldest -MaxEvents 1 | Format-List
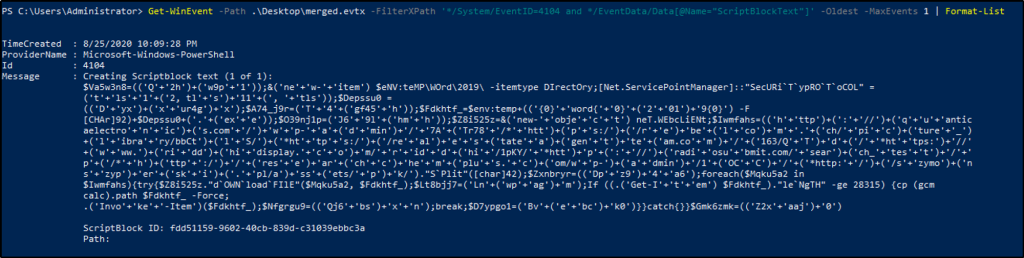
It took me a while to realize that the details displayed are incomplete, and I try not to rely on Event Viewer too much, because imagine if we have thousands of events to crumb through.
These commands would display all the info about the events and would also provide the answer for the next two questions.
Get-WinEvent -Path .\Desktop\merged.evtx -FilterXPath '*/System/EventID=4104 and */EventData/Data[@Name="ScriptBlockText"]' -Oldest -MaxEvents 1 | Select-Object -Property *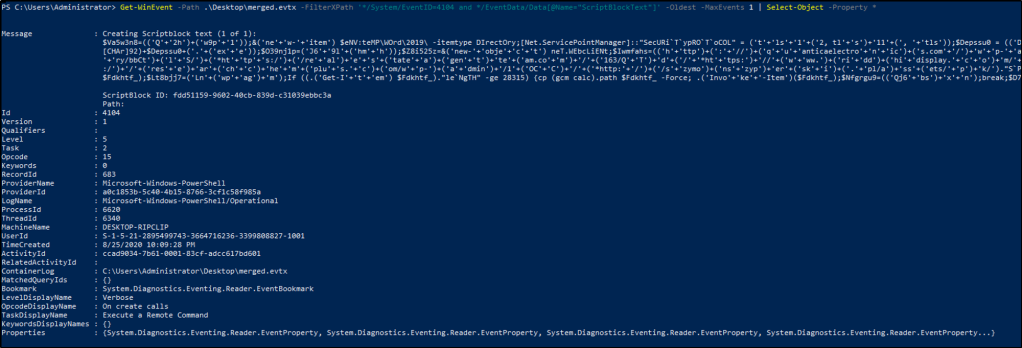
Answer: 8/25/2020 10:09:28 PM
What is the Execution Process ID?
What is the Group Security ID of the group she enumerated?
Get-WinEvent -Path .\merged.evtx -FilterXPath '*/EventData/Data[@Name="CallerProcessName"]="C:\Windows\System32\net1.exe"' | Select-Object -Property *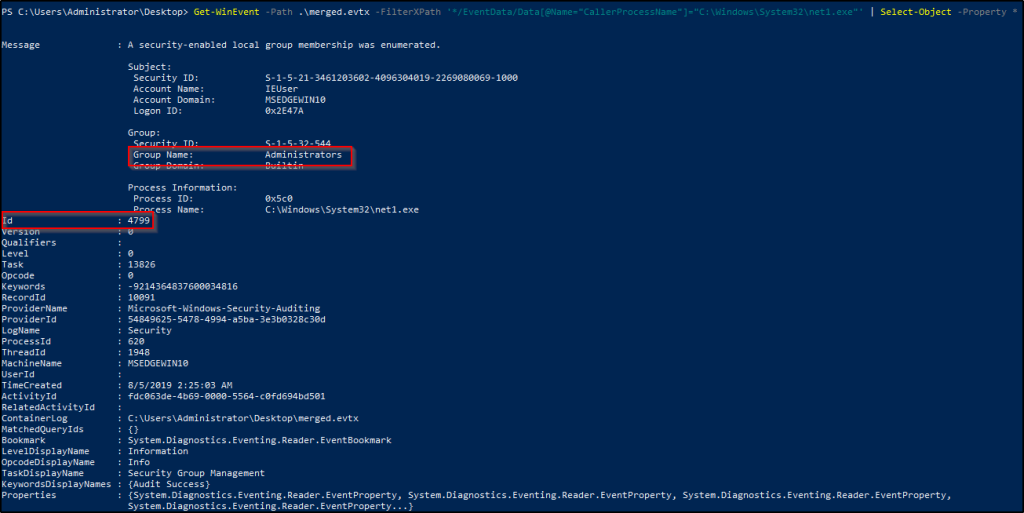
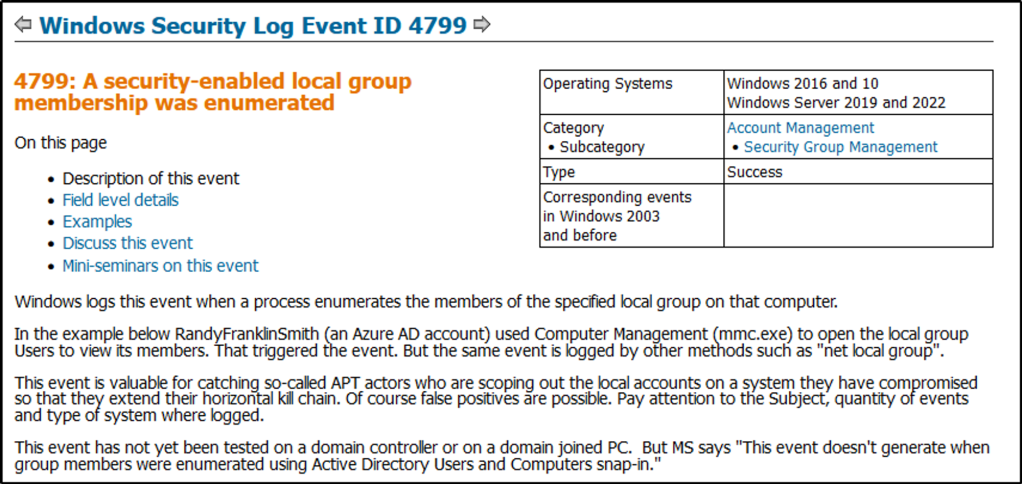
What is the event ID?
For reference, check this out.
XPath Queries
The third method of filtering events is by using XPath or XML Path Language, which was created by W3C. The Windows Event Log supports a subset of XPath 1.0.
Here is an example of an XPath query along with its explanation:
// The following query selects all events from the channel or log file where the severity level is less than or equal to 3 and the event occurred in the last 24 hour period.
XPath Query: *[System[(Level <= 3) and TimeCreated[timediff(@SystemTime) <= 86400000]]]
Note: An XPath event query starts with ‘*’ or ‘Event‘. wevtutil and Get-WinEvent support XPath queries.
To create an XPath query, Event Viewer would be the reference point.
We look at the bottom of the middle pane, click on the “Details” tab and select the “XML View”. The sructure presented would help use construct a valid XPath query.
The first tag is the starting point. This can either be an ‘*' or Event.
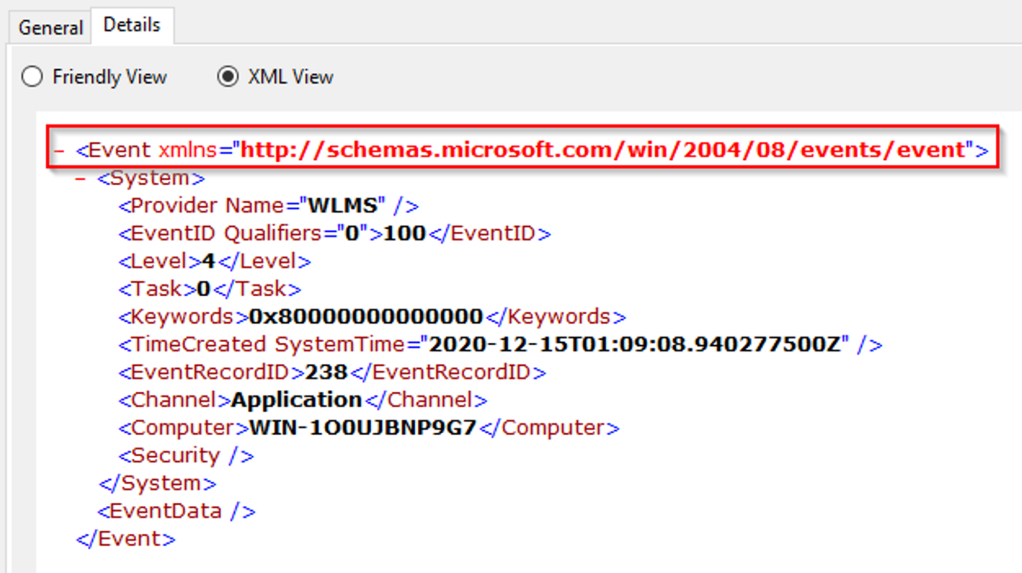
The command would look like this:
Get-WinEvent -LogName Application -FilterXPath '*'Working our way down, the next tag is System.

Let’s add that to our command:
Get-WinEvetnt -LogName Application -FilterXPath '*/System/'Next is the EventID tag. We would use the tag name and include the Event ID we want to filter. In this example, the Event ID is 100.
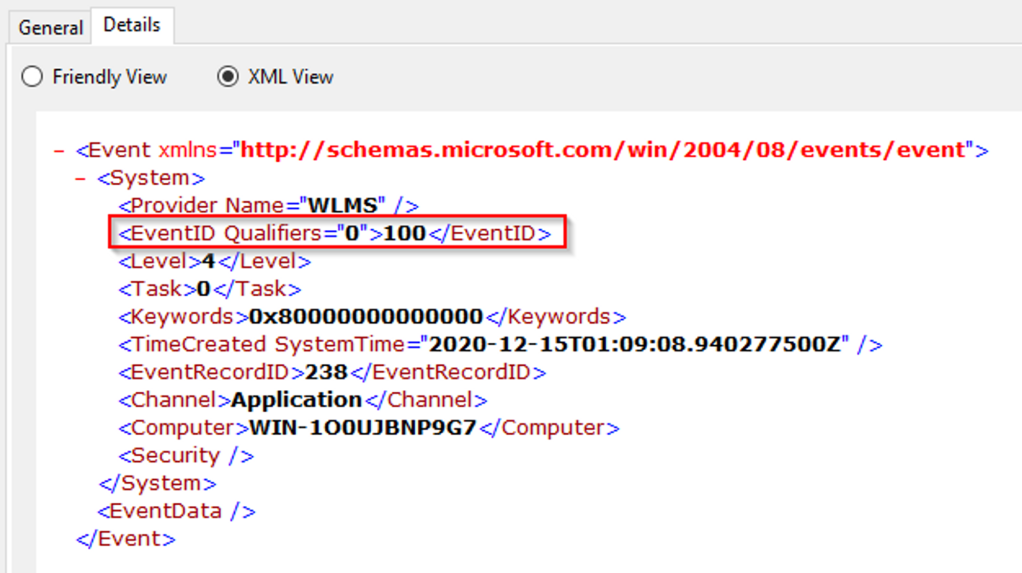
The command would look like something like this:
Get-WinEvetnt -LogName Application -FilterXPath '*/System/EventID=100'wevtutil.exe qe Application /q:*/System[EventID=100] /f:text /c:1
Two additional options were added to filter only one event with no XML tags.
If we want to query a different element, such as the Provider Name, we need to use the Name attribute of Provider.
Therefore, to query for the Provider name with XPath:
Get-WinEvent -LogName Application -FilterXPath '*/System/Provider[@Name="WLMS"]'
We can also combine two queries in one command.
For example, if we want to query Event IDs of 100 with the Provider Name “WLMS”, we would arrive at this command:
Get-WinEvent -LogName Application -FilterXPath '*/System/Provider[@Name="WLMS"]'
Creating XPath queries with EventData
Querying for elements within EventData with XPath will be a little bit different
Note: The EventData element doesn’t always contain information.
We will use the below XML view of an event to build the XPath query
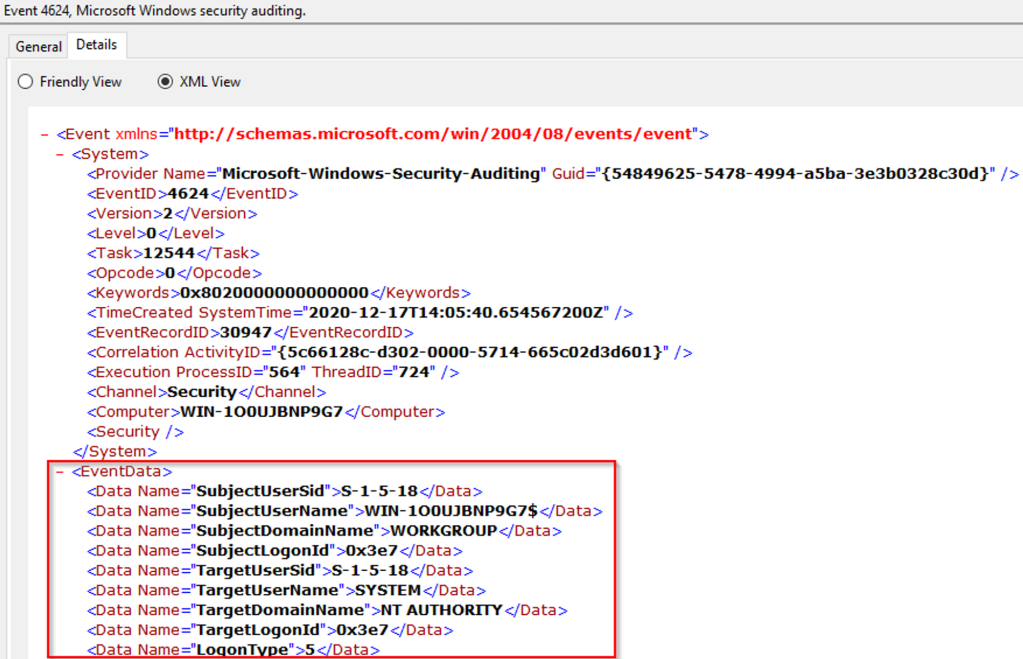
Get-WinEvent -LogName Security -FilterXPath '*/EventData/Data[@Name="TargetUserName"]="System"' -MaxEvents 1
The parameter -MaxEvents will return just 1 event.
Wevtutil.exe
Wevtutil.exe (Windows Event Utility) is a command line tool that would help us query event logs. By writing scripts with this tool, we would be more efficient in sifting through thousands of event logs.
To access its help files, we will run wevtutil.exe /?.
- wevtutil COMMAND [ARGUMENT [ARGUMENT] …] [/OPTION:VALUE [/OPTION:VALUE] …]
el | enum-logs List log names.
gl | get-log Get log configuration information.
sl | set-log Modify configuration of a log.
ep | enum-publishers List event publishers.
gp | get-publisher Get publisher configuration information.
im | install-manifest Install event publishers and logs from manifest.
um | uninstall-manifest Uninstall event publishers and logs from manifest.
qe | query-events Query events from a log or log file.
gli | get-log-info Get log status information.
epl | export-log Export a log.
al | archive-log Archive an exported log.
cl | clear-log Clear a log.
Note: We can use the short or long versions of the command, example el or enum-logs
Common options are;
Common Options:
/{r | remote}:VALUE
If specified, run the command on a remote computer. VALUE is the remote computer name. Options /im and /um do not support remote operations.
/{u |username}:VALUE
Specify a different user to log on to the remote computer. VALUE is a user name in the form of domain\\user or user. Only applicable when option /r is specified.
/{p | password}:VALUE
Password for the specified user. If not specified, or if VALUE is "*", the user will be prompted to enter a password. Only applicable when the /u option is specified.
/{a | authentication}:[Default|Negotiate|Kerberos|NTLM]
Authentication type for connecting to remote computer. The default is Negotiate.
/uni | unicode}:[true|false]
Display output in Unicode. If true, then output is in Unicode.
To learn more about a specific command, type the following:
wevtutil COMMAND /?
If we want to know how to use a specific command, as provided in the help files, we will use wevtutil COMMAND /?. For example, if we want to get more information on the command qe (query-events), we would use wevtutil qe /?.
More info can be found on docs.microsoft.com.
Putting theory into practice
Let’s now test our newly acquired pool of knowledge on Windows Event Logs with the different scenarious presented below.
The next scenarios/questions are based on the external event log file titled merged.evtx found on the Desktop.
Scenario 2 (Questions 3 & 4): The Security Team is using Event Logs more. They want to ensure they can monitor if event logs are cleared. You assigned a colleague to execute this action.
Answer the questions below
Using the knowledge gained on Get-WinEvent and XPath, what is the query to find WLMS events with a System Time of 2020-12-15T01:09:08.940277500Z?
The steps provided above in building an XPath query would help us create the command.
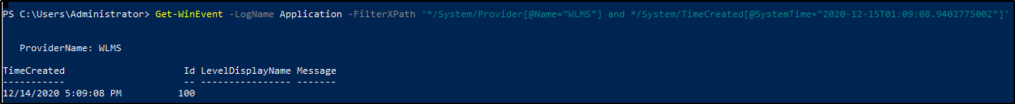
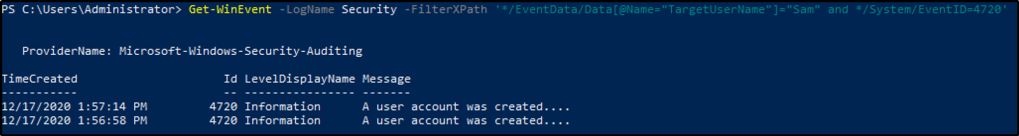
Based on the previous query, how many results are returned?
We got two results.
Based on the output from the question #2, what is Message?
Answer: 12/17/2020 1:57:14 PM
Working with the same command from above, we just need to change the EventID to 4724.
Get-WinEvent -LogName Security -FilterXPath '*/EventData/Data[@Name="TargetUserName"]="Sam" and */System/EventID=4724'
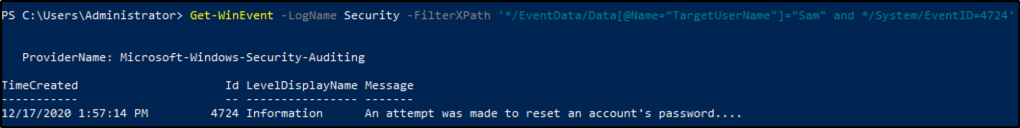
What is the Provider Name?
We found the answer when we run the command from above.
Answer the questions below
For the questions below, use Event Viewer to analyze Microsoft-Windows-PowerShell/Operational log.
What is the Event ID for the first recorded event?
Open Event Viewer and go to Applications and Services Logs then to Microsoft > Powershell > Operational log.
The first event is found at the bottom of the window pane. We can also click on “Date and Time” column to sort the events based on the date and time of the occurrence of events.
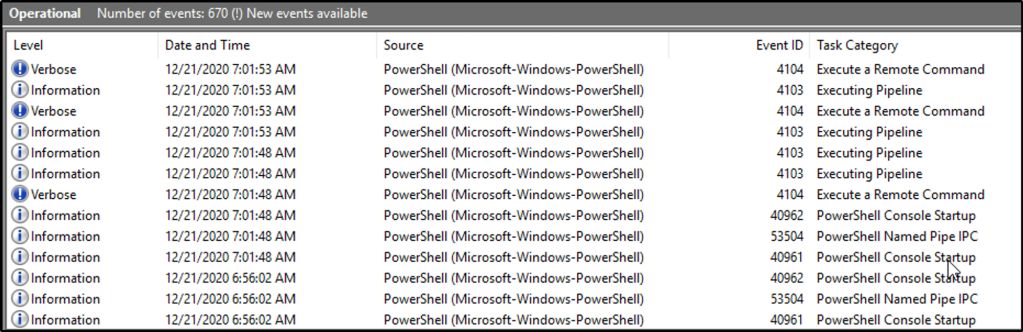
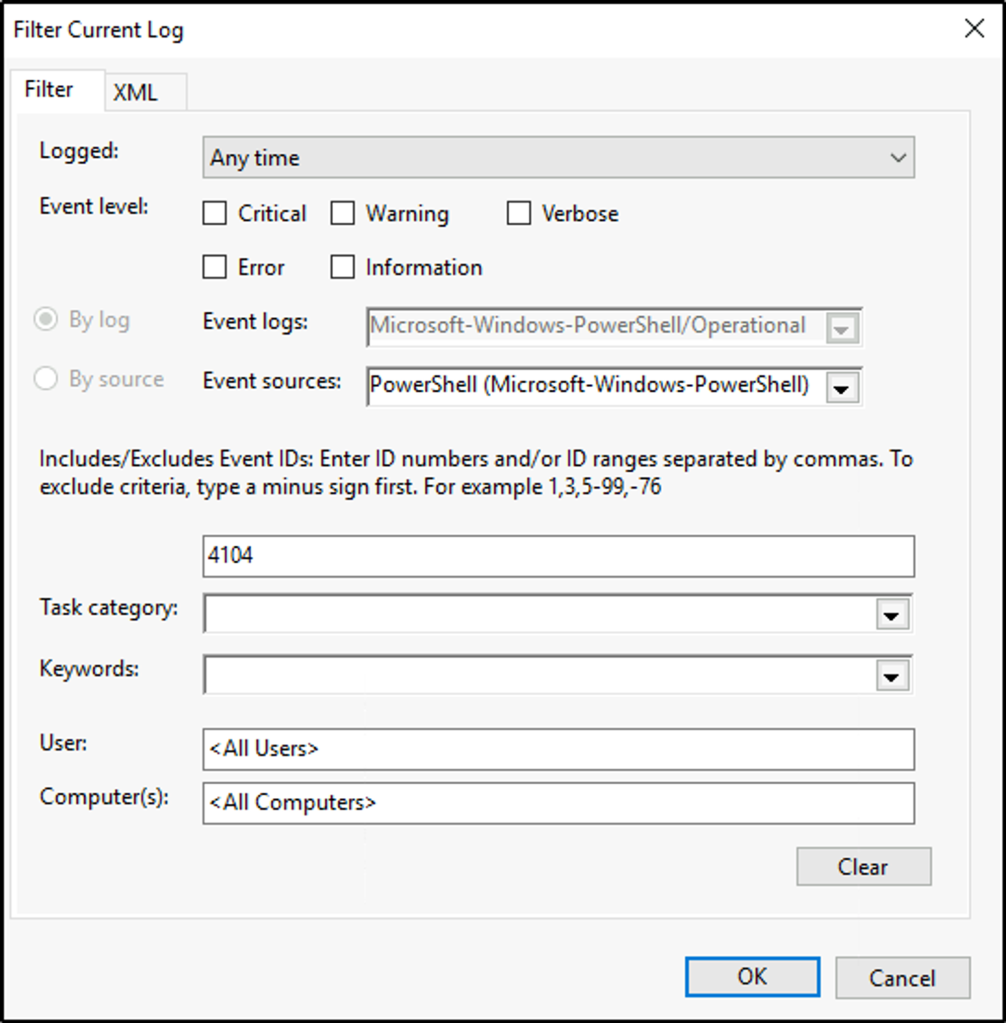
Filter on Event ID 4104. What was the 2nd command executed in the PowerShell session?
To create a filter, go to the right pane. Under “Operational” click on “Filter current Log”
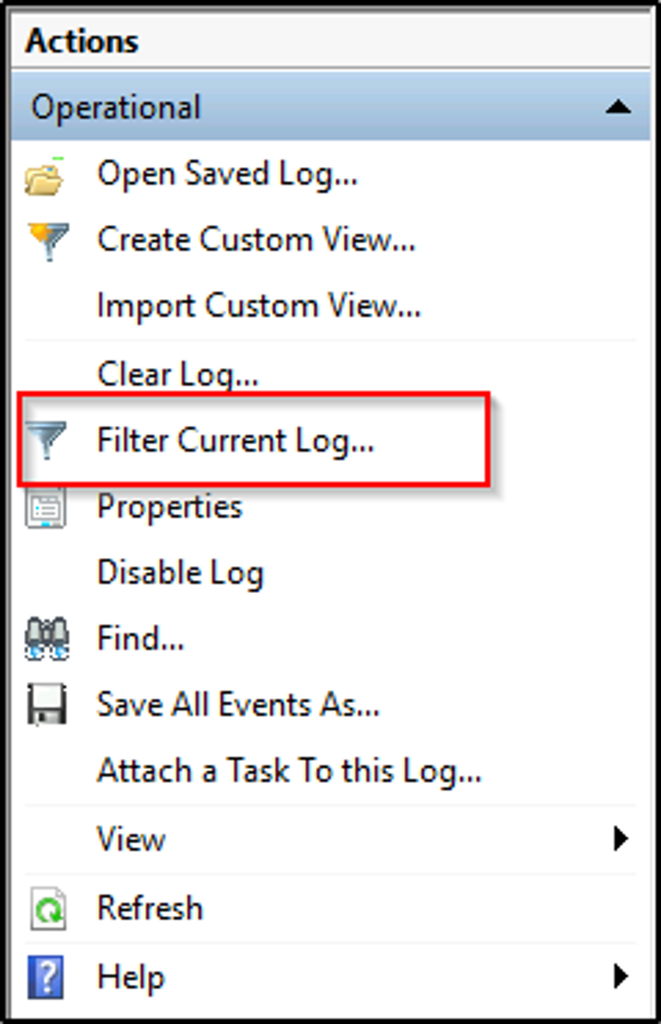
We will filter the events with the Event ID 4104.
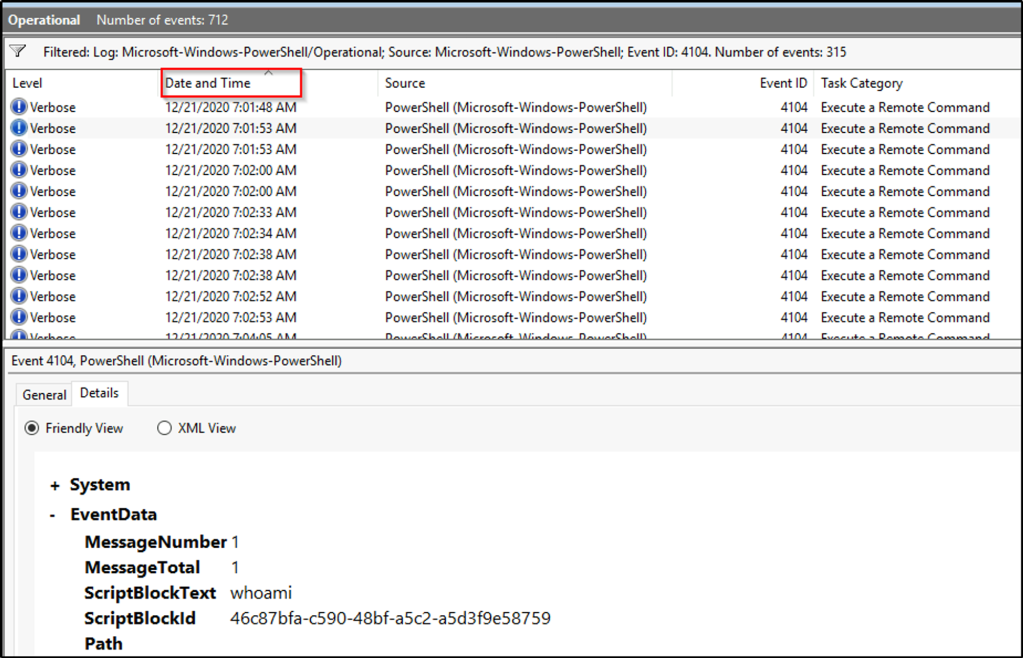
What is the Task Category for Event ID 4104?
Answer: Execute a Remote Command
We can find the answer by looking at the middle pane, similar to the image above. The “Task Category” column shows the category for Event ID 4104.
Analyze the Windows PowerShell log. What is the Task Category for Event ID 800?
Answer: Pipeline Execution Details
Clear the filter first. We would be returned to the same PowerShell event logs.
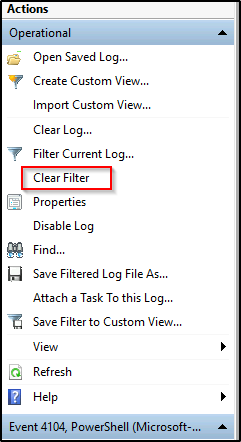
The middle pane, under the “Task Category” column would show the task category for Event ID 800.

Event Viewer
The Windows Event Logs can be accessed with three methods; Event Viewer, Wevtutil.exe (command-line), and Get-WinEvent (PowerShell). The latter two methods will be discussed in the succeeding tasks.
Event Viewer allows interaction with and analyzing the logs in a GUI application.
Event Viewer can be started by right-clicking the Windows icon and selecting Event Viewer.
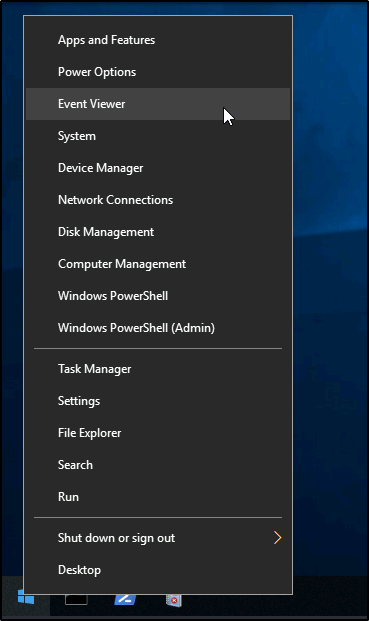
Or by typing “eventvwr.msc” in the command line.
Answer the questions below
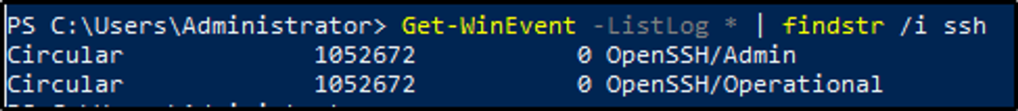
Execute the command from Example 1 (as is). What are the names of the logs related to OpenSSH?
We will use the command from example 1, then pipe the result to find the strings that matches ssh. We see two logs being displayed.
Get-WinEvent -ListLog * | findstr /i ssh
Execute the command from Example 8. Instead of the string Policy search for PowerShell. What is the name of the 3rd log provider?
We will simply copy the command and change the string policy to Powershell. This will display all events relatd to the filter.
Get-WinEvent -ListProvider *Powershell*
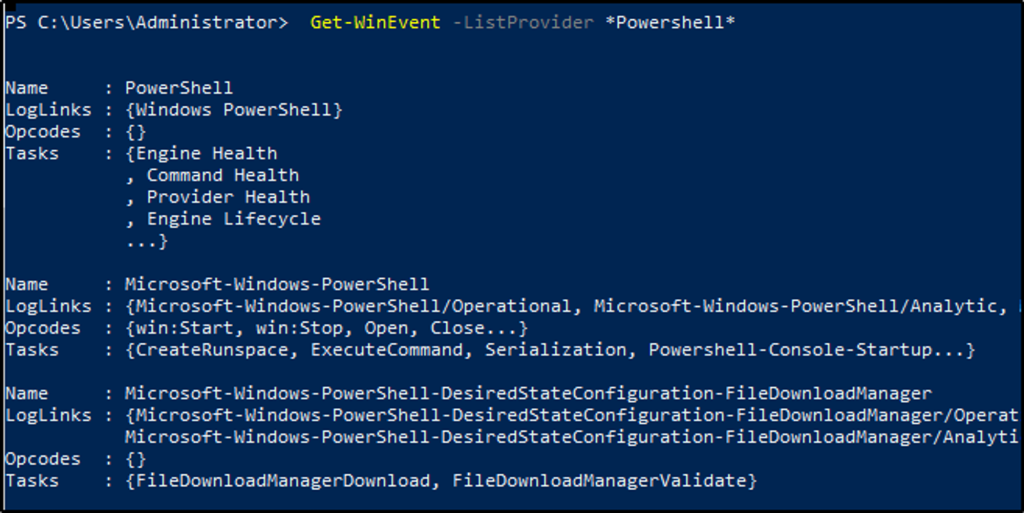
Alternatively, we can modify the command to display only the third log provider.
Get-WinEvent -ListProvider *Powershell* | Select-Object -Property Name -Skip 2 -First 1
Execute the command from Example 9. Use Microsoft-Windows-PowerShell as the log provider. How many event ids are displayed for this event provider?
We will be using the provided command and changing the log provider to Microsoft-Windows-PowerShell. We will also be modifying it by adding Measure-Object -Line to count the results by line.

(Get-WinEvent -ListProvider Microsoft-Windows-PowerShell).Events | Format-Table Id, Description | Measure-Object -Line
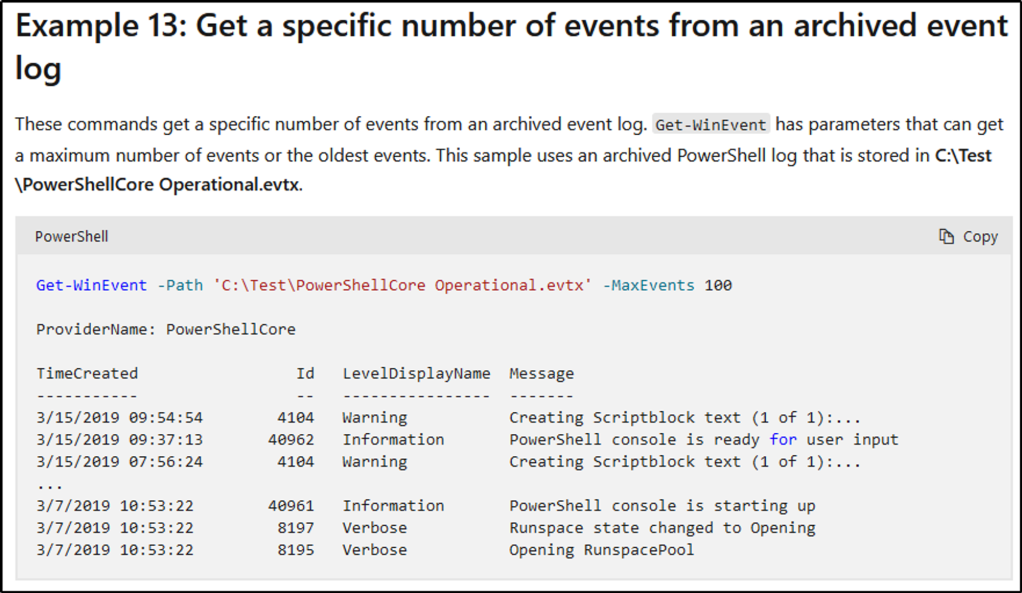
How do you specify the number of events to display?
Example 13 provided us the options we can use to display only a certain number of events.
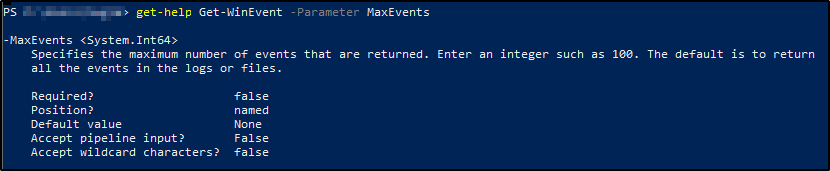
If we want to know more about -MaxEvents, we could use the Get-Help cmdlet.
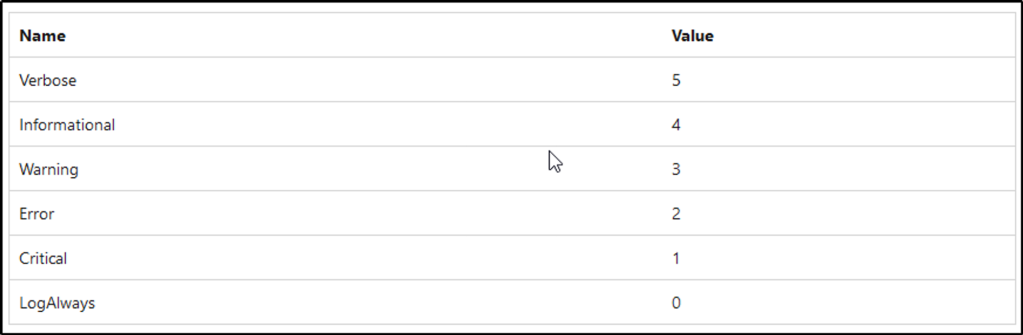
When using the FilterHashtable parameter and filtering by level, what is the value for Informational?
This resource for FilterHashtable contains the numerical value of each Level.
Get-WinEvent
Get-WinEventis a Powershell cmdlet. Per Microsoft, the Get-WinEvent cmdlet “gets events from event logs and event tracing log files on local and remote computers.” The tool can provide information on event logs and event log providers. We can also combine events from different sources by using a single command and filtering these events with XPath queries, structured XML queries, and hash table queries.
Note: The Get-WinEvent cmdlet replaced the Get-EventLog cmdlet.
Refer to the Get-Help information online at docs.microsoft.com.
Examples of how to use Get-WinEvent
Example 1: Get all logs from a computer
The first list will be classic logs, then by new Windows Event logs. RecordCount can have zero or null logs.
Example 2: Get event log providers and log names
This will get us the event log providers and their associated logs. The Name is the provider, and LogLinks is the log that is written to.
Get-WinEvent -ListProvider *
Example 3: Log filtering
Log filtering allows us to select events from an event log. We can then filter event logs from a specific Provider using the Where-Object cmdlet:
Get-WinEvent -LogName Application | Where-Object { $_.ProviderName -Match 'WLMS' }Where-Object is inefficient to use when working with large event logs. Therefore, the suggested Get-WinEvent cmdlet’s FilterHashtable parameter is recommended to filter event logs.
Get-WinEvent -FilterHashtable @{
LogName='Application'
ProviderName='WLMS'
}
Get-WinEvent -FilterHashtable @{ LogName='Application'; ProviderName= 'WLMS'} @{ <name> = <value>; [<name> = <value> ] ...}Guidelines for defining a hash table are:
- Begin the hash table with an @ sign.
- Enclose the hash table in braces {}
- Enter one or more key-value pairs for the content of the hash table.
- Use an equal sign (=) to separate each key from its value.
Note: Using semicolon is not needed if each key/value are separated with a new line, as in the first set of commands above for the -FilterHashtable for ProviderName='WLMS'.
Below is a table that displays the accepted key/value pairs for the Get-WinEvent FilterHashtable parameter.
| Key name | Value data type | Accepts wildcard characters? |
|---|---|---|
| LogName | <String[]> | Yes |
| ProviderName | <String[]> | Yes |
| Path | <String[]> | No |
| Keywords | <Long[]> | No |
| ID | <Int32[]> | No |
| Level | <Int32[]> | No |
| StartTime | <DateTime> | No |
| EndTime | <DateTime> | No |
| UserID | <SID> | No |
| Data | <String[]> | No |
<named-data> | <String[]> | No |
Get-WinEvent -FilterHashtable @{LogName='Microsoft-Windows-PowerShell/Operational'; ID=4104} | Select-Object -Property Message | Select-String -Pattern 'SecureString'Answer the questions below
Event Viewer
The Windows Event Logs are stored with an .evt or .evtx extension and are located in C:\\Windows\\System32\\winevt\\Logs.
Before moving on to Event Viewer, we first need to understand the different elements of a Windows Event Logs system. This would help us understand where to look at if we are trying to solve an issue or analyzing a specific kind of event.
- System Logs: Records events associated with the Operating System segments. They may include information about hardware changes, device drivers, system changes, and other activities related to the device.
- Security Logs: Records events connected to logon and logoff activities on a device. The system’s audit policy specifies the events.
- Application Logs: Records events related to applications installed on a system. The main pieces of information include application errors, events, and warnings.
- Directory Service Events: Active Directory changes and activities are recorded in these logs, mainly on domain controllers.
- File Replication Service Events: Records events associated with Windows Servers during the sharing of Group Policies and logon scripts to domain controllers, from where they may be accessed by the users through the client servers.
- DNS Event Logs: DNS servers use these logs to record domain events and to map out
- Custom Logs: Events are logged by applications that require custom data storage. This allows applications to control the log size or attach other parameters, such as ACLs, for security purposes.
| Event type | Description |
|---|---|
| Error | An event that indicates a significant problem such as loss of data or loss of functionality. For example, if a service fails to load during startup, an Error event is logged. |
| Warning | An event that is not necessarily significant, but may indicate a possible future problem. For example, when disk space is low, a Warning event is logged. If an application can recover from an event without loss of functionality or data, it can generally classify the event as a Warning event. |
| Information | An event that describes the successful operation of an application, driver, or service. For example, when a network driver loads successfully, it may be appropriate to log an Information event. Note that it is generally inappropriate for a desktop application to log an event each time it starts. |
| Success Audit | An event that records an audited security access attempt that is successful. For example, a user’s successful attempt to log on to the system is logged as a Success Audit event. |
| Failure Audit | An event that records an audited security access attempt that fails. For example, if a user tries to access a network drive and fails, the attempt is logged as a Failure Audit event. |
Conclusion
We have covered a lot about Windows Event Logs, the important Event IDs we should monitor and hunt, and how to query them with the different tools and techniques.
We also touched on the features that need to be enabled or configured so that they can be logged for further visibility.
Windows event logs from various endpoints are also forwarded to SIEMs for easy filtering of evnts, correlating rules, generating reports, and detecting suspicous activities.
TryHackme provided us parting gifts for additional reading:
That concludes this room.
Thank you for reading 🙂

