

Когда у вас есть сразу несколько серверов WSUS с центральным корневым, бывает очень проблематично получать отчеты об обновлениях рабочих станций.
Мне был нужен скрипт, который покажет, что на каких-то компьютерах есть не установленные одобренные обновления. Такой отчет есть в консоли WSUS, он называется Computer Tabular Status for Approved Updates.
Но это достаточно трудоемкая задача, когда у вас 5-10-15 серверов.
Instructions
1. TypeStart PowerShellin theCommand Promptwindow to startWindows PowerShell.
2. TypeInstall-WindowsFeature UpdateServices and pressEnterto install theWSUSrole.

The WID Database and WSUS Services role services are installed after running the Install-WindowsFeature UpdateSevices
Adds a specified client computer to a specified target group.
Approve-WsusUpdate – Approves an update to be applied to clients.
Deny-WsusUpdate – Declines the update for deployment.
Get-WsusClassification – Get the list of all WSUS classifications currently available in the system.
Get-WsusComputer – Gets the WSUS computer object that represents the client computer.
Get-WsusProduct – Get the list of all products currently available on WSUS by category.
Get-WsusServer – Gets the value of the WSUS update server object.
Get-WsusUpdate – Gets the WSUS update object with details about the update.
Invoke-WsusServerCleanup – Performs the process of cleanup on a specified WSUS server.
Set-WsusClassification – Sets whether the classifications of updates that WSUS synchronizes are enabled or disabled.
Set-WsusProduct – Sets whether the product representing the category of updates to synchronize is enabled or disabled.
Set-WsusServerSynchronization – Sets whether the WSUS)server synchronizes from Microsoft Update, or an upstream server and the upstream server properties.
This article discusses the “Windows Server Update Services is not installed” error message you get when installing the Patch My PC Publisher.
Topics covered in this article:
- Introduction
- How to fix it
Introduction
When you install the Patch My PC Publisher on a Windows 10 / 11 / Windows Server, you get the error message “Windows Server Update Services is not installed”.
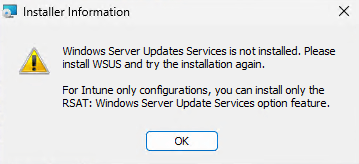
Even for the Intune-only integration, the Patch My PC Publisher can only be installed if the WSUS RSAT tools are installed. These tools are needed to be installed to parse the Patch My PC catalog XML.
How to fix it
If you are installing the Patch My PC Publisher on a , you’ll need to install the WSUS RSAT tools to fix this issue.
 Note: You can only install the WSUS RSAT tools on Pro or Enterprise Operating Systems.
If you plan on installing the Publisher on a Windows Server OS, you’ll need to install the .
Note: It’s not mandatory to install the full WSUS role, the API is sufficient.
How to fix the issue on Windows 10 and Windows 11 OS
- Open an elevated PowerShell window.
- Enter this command:
Add-WindowsCapability -Online -Name Rsat.WSUS.Tools~~~~0.0.1.0
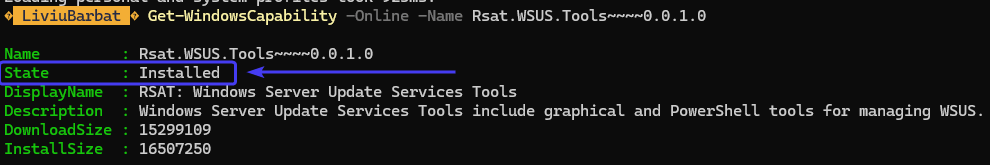
Get-WindowsCapability -Online -Name Rsat.WSUS.Tools~~~~0.0.1.0
You should get a result similar to this:
How to fix the issue on a Windows Server OS
- Open an elevated PowerShell window.
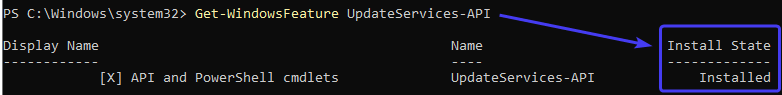
- Enter this command:
You should get a result similar to this:
Инструкции
1. ВведитеStart PowerShellвокне командной строки,чтобы запустить оболочкуWindows PowerShell.
2. ВведитеInstall-WindowsFeature UpdateServices и нажмитеклавишу Enter, чтобы установить рольWSUS.

Службы ролей WSUS можно установить с помощьюWindows PowerShell
- База данных WID
База данных WID и службы ролей служб WSUS устанавливаются после выполнения Install-WindowsFeature UpdateEvavices.
командлеты Windows PowerShellдоступны для управления рольюWSUS на сервере под управлением Windows Server Core.
добавление указанного клиентского компьютера в указанную целевую группу.
Approve-WsusUpdate — утверждение обновления, применяемого к клиентам.
Deny-WsusUpdate — отклоняет обновление для развертывания.
Get-WSUSCLASSIFICATION — получение списка всех классификаций WSUS, доступных в данный момент в системе.
Get-WsusComputer — получает объект компьютера WSUS, представляющий клиентский компьютер.
Get-WsusProduct — получение списка всех продуктов, доступных в настоящее время в WSUS, по категориям.
Get-WsusServer — получает значение объекта сервера обновлений WSUS.
Get-WsusUpdate — возвращает объект обновления WSUS с подробными сведениями об обновлении.
Invoke-WsusServerCleanup — выполняет процесс очистки на указанном сервере WSUS.
Set-WSUSClassification — указывает, включены или отключены классификации обновлений, синхронизируемые WSUS.
Set-WsusProduct — указывает, включен или отключен продукт, представляющий категорию синхронизируемых обновлений.
Set-WsusServerSynchronization — определяет, будет ли сервер WSUS синхронизироваться с Центром обновления Майкрософт или с вышестоящим сервером и свойствами вышестоящего сервера.
Many IT professionals use Windows Software Update Services (WSUS) to manage updates across all their Windows systems and other third-party software. When paired up with PowerShell, managing updates becomes even quicker and more efficient.
WSUS monitors for and installs updates while PowerShell makes syncing them from Microsoft easy. You can also use PowerShell to make checking the status of the computers you’re managing more straightforward and adaptable.
WSUS isn’t just for Windows. It can also manage updates for some third-party software as well as Office products, SQL Server and Exchange Server.
How to use PowerShell to manage WSUS
Below, find out how to sync your WSUS server with Microsoft update, how to query all the computers your WSUS server is managing, and how to use PowerShell commands in WSUS.
1. Sync your WSUS server with Microsoft Update.
One way to remotely connect to a WSUS server is to use PowerShell remoting, so make sure that your WSUS server has this enabled. PowerShell remoting is a feature that allows you to run commands on a remote computer as if you were logged in locally. This is useful for managing WSUS servers from anywhere without having to use Remote Desktop or other tools.
Keep your WSUS server consistently synchronized with Microsoft Update to help maintain a secure, up-to-date and reliable Windows infrastructure.
Now that you have enabled PowerShell remoting, connect to your WSUS server using the PowerShell cmdlet Enter-PSSession.
Keep in mind that you’re entering an interactive remoting session to demonstrate some commands. You may also use the Invoke-Command command to automate many of these commands in a larger script.
First, determine how to query all updates currently on our WSUS server. To do that, use the Get-WsusUpdate command. When this command is run on a new WSUS server, you’ll see that nothing is returned. This is because no updates have been synchronized yet. Initiate a sync from PowerShell using the Get-WsusServer cmdlet.
Once complete, all updates that were configured to sync should be downloaded locally. Once you’ve ensured all patches are synced with Microsoft Update, look at all of the clients this server is currently managing updates on.
Use the Get-WsusComputer command to get an overview of all the computers your WSUS server is managing.
2. Query all of the computers that your WSUS server is managing.
Last status report | |||
|---|---|---|---|
1/1/0001 12:00:00 AM |
To get a full listing of all of the commands available to you, use the Get-Command command. You then can view a list of all of the WSUS commands inside of the WSUS module.
Periodically export your WSUS settings as part of your disaster recovery and business continuity plans. Ready access to these settings can improve recovery time significantly in case of a server failure or other issues.
Once you have your WSUS server configured the way you’d like, you can also manage the WSUS clients. Although Microsoft doesn’t give you a good option to do this via PowerShell, you can rely on the community and download a module from Github called WindowsUpdate. Once installed, this module allows you to query remote computers for installed updates, install required updates, and more. Here’s how to download and install it:
3. Use PowerShell commands in WSUS.
Once the module is installed, you’ll have multiple commands available to you.
PS C:> gcm -Module windowsupdate
Let’s say you’d like to see what updates are installed on that computer you referenced earlier on the server. To do that, use the Get-WindowsUpdate command:
PS> Get-WindowsUpdate -ComputerName client1
PS> Install-WindowsUpdate -ComputerName client1 -ForceReboot
One of the great things about managing WSUS with PowerShell is that you can extend the functionality in any way you’d like. So, for example, you could stitch these commands together and perhaps take a list of computers from a text file, add them to a WSUS target group, and invoke an update install all in one script.
By using the PowerShell commands that Microsoft provides as well as a community resource module, you open up many possibilities. If you haven’t used PowerShell to manage WSUS yet, give it a try. You’ll see how much time you can save by automating manual processes.
Leveraging PowerShell to manage WSUS can save you considerable time and effort. It also gives you the flexibility to extend functionality according to your needs.
More ways to use PowerShell
PowerShell is worth learning. It’s not as hard to absorb as many coding languages, and mastering it can help simplify and automate a lot of the necessary-but-unproductive IT jobs in your business. Check out our other articles below to find out more:
Mark Fairlie contributed to this article.
Скрипт
На строках 2, 4 и 7 находятся переменные, которые можно менять по необходимости.
$datetime = Get-Date -Format "yyyy.MM.dd_HH-mm-ss";
$domain = "domain.local";
$serverName = "wsus10.domain.local";
$file_name = "wsus_audit_result_" + $domain + "_" + $datetime + ".csv";
$xl_filename = "c:\audit\" + $file_name;
[void][reflection.assembly]::LoadWithPartialName("Microsoft.UpdateServices.Administration")
$wsus = [Microsoft.UpdateServices.Administration.AdminProxy]::getUpdateServer($serverName, $false)
$computerscope = New-Object Microsoft.UpdateServices.Administration.ComputerTargetScope
$computerscope.IncludeSubgroups = $true;
$computerscope.IncludeDownstreamComputerTargets = $true;
$computerscope.IncludedInstallationStates = [Microsoft.UpdateServices.Administration.UpdateInstallationStates] "Failed, NotInstalled, Downloaded";
$updates = $wsus.GetUpdates() | where {$_.IsApproved -eq $true};
$array = @{};
foreach ($update in $updates) {	$temp = $update.GetUpdateInstallationInfoPerComputerTarget($ComputerScope) | ?{$_.UpdateApprovalAction -eq "Install"}	if ($temp -ne $null) {	foreach ($item in $temp) {	$array.($wsus.GetComputerTarget([guid]$item.ComputerTargetId).FulldomainName)++;	}	}
}
$export_array = @();
$export_array += ,@("");$export_array += ,@("");
$i = 1;
foreach ($key in $array.Keys)
{	if ($key.split(".")[1] -eq $domain.split(".")[0]) {	$export_array += ,@($key.Split(".")[0], $key.Split(".")[1], $array.$key);	}
}
Write-Output "Saving report ...";
foreach($item1 in $export_array)
{	$csv_string = "";	foreach($item in $item1)	{	$csv_string = $csv_string + $item + ";";	}	Add-Content $xl_filename $csv_string;
}
Отработка команд занимает достаточно продолжительное время, т.к. для каждого компьютера, зарегистрированного в WSUS, делается запрос на сервер по HTTP-протоколу. Это достаточно медленная процедура. Поэтому придется подождать.
Не пытайтесь запустить скрипт на обычном сервере или компьютере. Корректно работать он будет только на сервере, где установлена консоль управления WSUS.
Просмотров: 9966
Решение
Я написал скрипт в среде Powershell, который автоматизирует задачу получения отчетов из WSUS.
Скрипт лучше всего запускать на центральном управляющем сервере WSUS, т.к. он содержит все сведения обо всех компьютерах всех серверов обновлений WSUS. Однако можно запустить и на рядовом сервере. Отчет, естественно, вы получите только для компьютеров, подключенных к этому серверу.


